Auth0Alternatives
FeaturesOpen SourceSelf-hostedB2BB2C
SubmitSign In

Discover

LatestOpen SourceSelf-hostedB2BB2CAll providers

AI & Agents

MCP AuthorizationAgent IdentitiesToken VaultAI Agent DetectionDevice LoginAll features

Data Residency

🇪🇺European Union🇺🇸United States🇬🇧United Kingdom🇨🇭Switzerland🇦🇺AustraliaAll regions

Compliance

SOC2GDPRISO 27001HIPAAPCI DSSAll compliance
Submit
Favicon of MojoAuth

MojoAuth

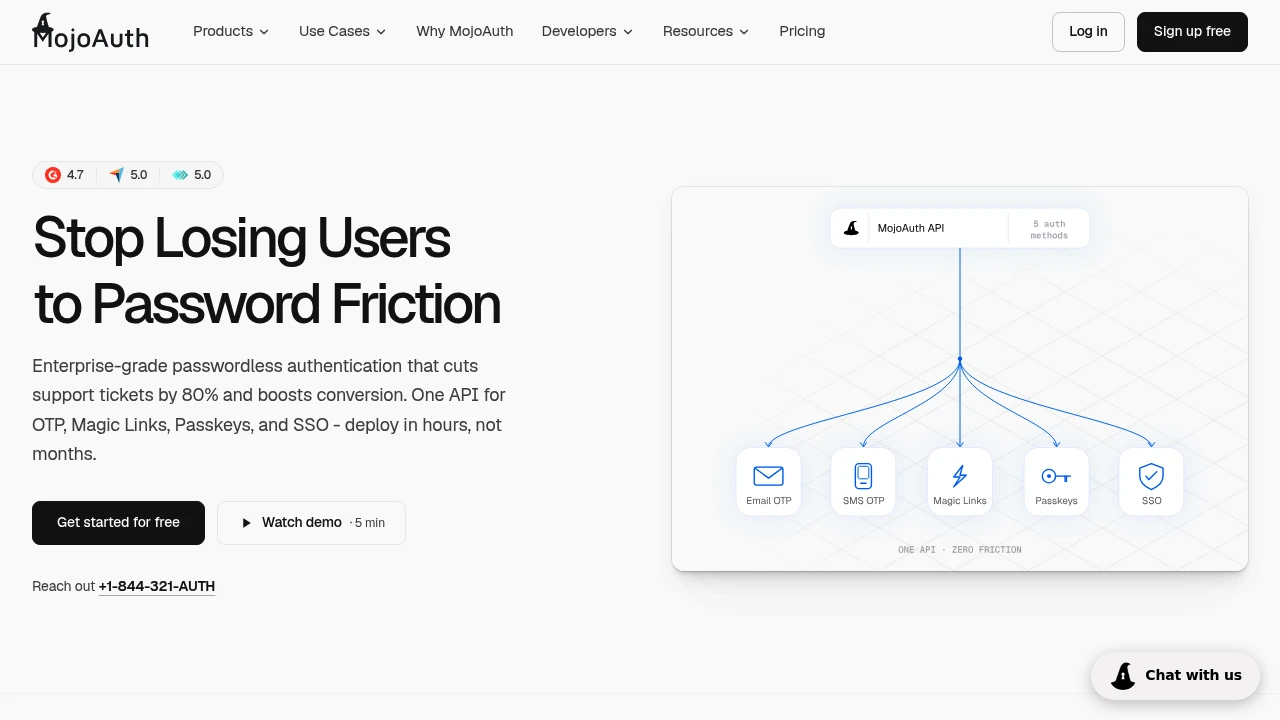
Enterprise-grade passwordless authentication that cuts support tickets by 80% and boosts conversion. One API for OTP, Magic Links, Passkeys, and SSO - deploy in hours, not months.
Visit MojoAuthauth0 iconCompare with Auth0
Screenshot of MojoAuth websiteVisit MojoAuth

MojoAuth is a passwordless authentication API built to eliminate password-related friction, breaches, and support overhead. With a zero-store architecture, no passwords are ever saved and there's no credential database to breach, removing one of the biggest security liabilities in modern apps.

A single, consistent API covers the full authentication toolkit:

  • Email, Phone, and WhatsApp OTP for flexible one-time password delivery
  • Authenticator OTP (TOTP) and HOTP for counter and time-based codes
  • Passkeys (FIDO2/WebAuthn), magic links, and social login
  • SSO and multi-factor authentication for layered security

Companies choose MojoAuth over building in-house because it cuts 3-6 months of engineering work down to hours or days of integration, while removing ongoing maintenance, compliance tracking, and security expertise burdens. It's GDPR and SOC 2 compliant, backed by a 99.99% uptime SLA on enterprise plans, and supports gradual migration alongside existing login systems via webhooks and RESTful APIs.

Trusted by 5,000+ businesses including Dell, Capgemini, Abbott, and Johnson & Johnson, MojoAuth processes over 14 million authentication requests daily. Teams report an 80% drop in support tickets and improved conversion after removing password friction. A free tier supports up to 25,000 monthly active users.

Features:

Passwordless Authentication
Social Connections
Passkeys
Long Lived Sessions
Session Management
Multi-Language
Device Login (CLI & TV)

SSO Enterprise Connections
SAML
SCIM
CIBA
LDAP

Client Credentials Support
Access Token Support
Token Restrictions

MCP Authorization
Agent Client Registration
Third-Party App & Agent Access

Standard scopes only, no custom scopes.

Token Vault
Human-in-the-Loop Approval
Agent Identities
Delegated Token Exchange
Developer MCP Server

Custom Login Page
Custom Domain

Webhooks
Integrations

Brute Force Protection
Suspicious IP Detection
Impossible Travel Protection
Bot Detection
Breached Password Protection
New Device Detection
MFA
Adaptive MFA
Security Monitoring Dashboard
AI Agent Detection
Fraud & Risk Scoring

Enterprise plan only, and only described on marketing pages.

User Import
Organizations
Custom Attributes
Role Management
Account Linking
Impersonation
Admin Interface
User Export
Password Export

Rate Limits
Log Streaming
Environments
SLA

Enterprise advertises 99.99% uptime and a one-hour critical-issue response SLA
Community Support
Email Support
Enterprise Support
Monitoring
Compliance:
ccpa iconCCPACompliantcsa-star iconCSA STARCertifiedgdpr iconGDPRComplianthipaa iconHIPAACompliantiso-27001 iconISO 27001Certifiedpci-dss iconPCI DSSCompliantsoc2 iconSOC2Compliant
Data Residency:
🌏Asia-Pacific🇪🇺European Union🌎Latin America🌍Middle East & Africa🇺🇸United States
Share:
Details:
  • B2B


    Yes
  • B2C


    Yes
  • Open Source


    No
  • Self-hosted


    Yes
  • EU data residency


    Yes
Favicon


Similar to MojoAuth:

Favicon


Favicon


Favicon


Subscribe to our newsletter

Join other CTOs and engineers to get the latest news and to keep your apps secure.

Browse:Open SourceSelf-hostedB2BB2CFeaturesComplianceData Residency
Quick Links:Contact UsSubmitBlogAbout Us
Built withDirstarter
Auth0Alternatives
FeaturesOpen SourceSelf-hostedB2BB2C
SubmitSign In

Discover

LatestOpen SourceSelf-hostedB2BB2CAll providers

AI & Agents

MCP AuthorizationAgent IdentitiesToken VaultAI Agent DetectionDevice LoginAll features

Data Residency

🇪🇺European Union🇺🇸United States🇬🇧United Kingdom🇨🇭Switzerland🇦🇺AustraliaAll regions

Compliance

SOC2GDPRISO 27001HIPAAPCI DSSAll compliance
Submit
Featured projects

Become a sponsor of Auth0Alternatives:

Favicon of DescopeFavicon of Authsignal

Similar to MojoAuth:

Favicon of Hexclave

Hexclave

Open-source platform for auth, users, payments and analytics
Hexclave (formerly Stack Auth) is an open-source authentication and user management platform with login pages, OAuth, RBAC, teams, payments and analytics. Open-source alternative to Auth0 and Clerk.
Open Source
Favicon of Hanko

Hanko

Modern authentication with passkeys, 2FA, and SSO
Open-source authentication platform offering passwordless login with passkeys, traditional passwords, 2FA, and SSO. Integrate secure user management in minutes.
Open Source
Favicon of FusionAuth

FusionAuth

Complete auth solution with hybrid deployment flexibility
Complete Customer Identity and Access Management (CIAM) platform with SSO, MFA, OAuth2, and OpenID Connect. Deploy anywhere with security-first design.
Popular Auth0 Comparisons:
Engity vs Auth0
Amazon Cognito vs Auth0
Entra External ID vs Auth0
Firebase Authentication vs Auth0
Clerk vs Auth0
WorkOS vs Auth0
Frontegg vs Auth0
FusionAuth vs Auth0
Supabase Auth vs Auth0
Auth.js vs Auth0
Ory vs Auth0
SuperTokens vs Auth0
Logto vs Auth0
Hanko vs Auth0
Hexclave vs Auth0
Authress vs Auth0
Popular WorkOS Comparisons:
Engity vs WorkOS
Auth0 vs WorkOS
Amazon Cognito vs WorkOS
Entra External ID vs WorkOS
Firebase Authentication vs WorkOS
Clerk vs WorkOS
Frontegg vs WorkOS
FusionAuth vs WorkOS
Supabase Auth vs WorkOS
Auth.js vs WorkOS
Ory vs WorkOS
SuperTokens vs WorkOS
Logto vs WorkOS
Hanko vs WorkOS
Hexclave vs WorkOS
Authress vs WorkOS
Ad
Favicon of DescopeDescope
Drag & Drop Your Auth. Add secure, frictionless authentication journeys for your customers, partners, and AI agents.
Visit Descope
Ad
Favicon of AuthsignalAuthsignal
You might not need to replace your auth provider. Add passkeys, adaptive MFA, and a no-code orchestration engine on top of the identity stack you already run.
Visit Authsignal