Sooauth
Open-source OIDC authentication with passkeys, no DB migrations, and 10-second self-hosting. Free cloud beta for AI builders and indie SaaS.
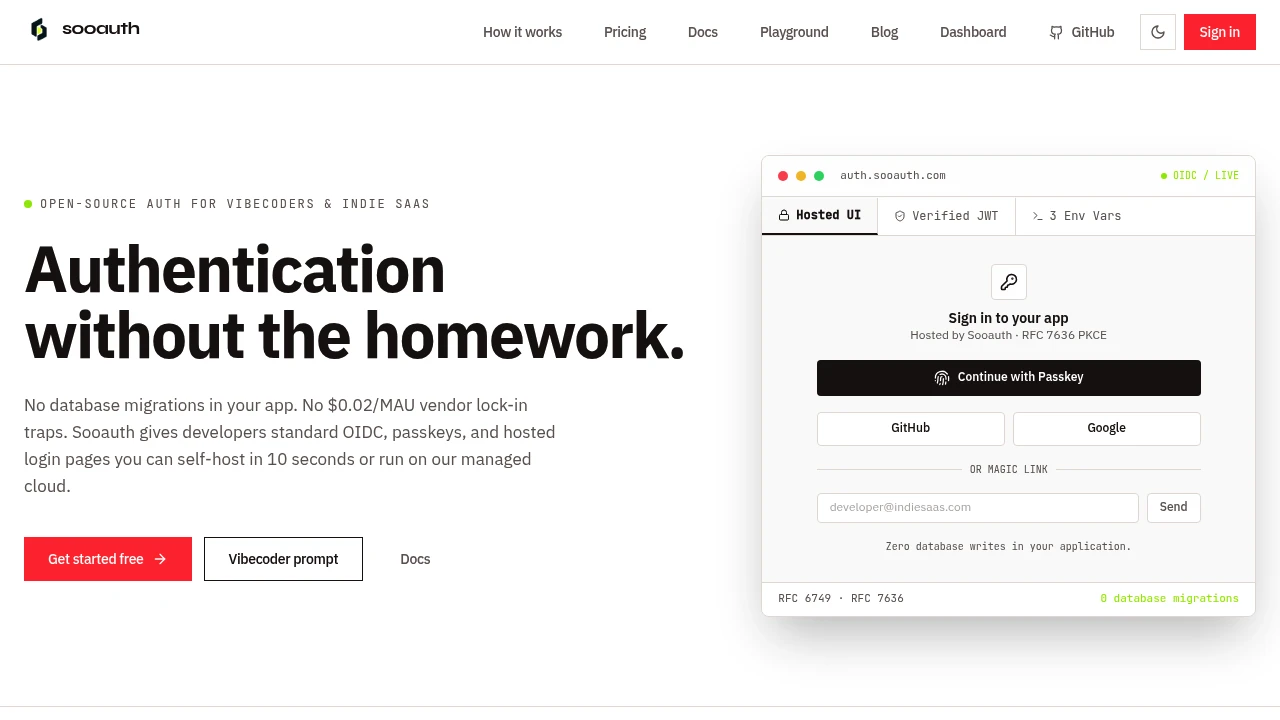
Sooauth is an open-source authentication layer built for vibecoders, AI-assisted developers, and indie SaaS teams who are tired of database migrations and MAU-based pricing traps. It runs entirely outside your application database — your app just verifies standard, signed OIDC tokens.
Because Sooauth speaks pure OpenID Connect (RFC 6749 / RFC 7636), tools like Cursor, Claude Code, Windsurf, and v0 can wire up authentication from a single prompt, with no hallucinated SDK calls or schema conflicts.
Key features:
- Zero database migrations — your app stays clean
- Standard OIDC discovery, authorize, token, userinfo, and JWKS endpoints
- Passkeys (WebAuthn), Google, and GitHub sign-in
- Self-host in 10 seconds via a single Docker install script
- Lightweight Go binary (~25MB) vs. Java-based alternatives
- Hosted cloud option at auth.sooauth.com, currently free during public beta
- AGPL-3.0 licensed, fully open source
Whether you start on the free hosted cloud or self-host on your own VPS with curl -sSL ... | bash, Sooauth uses the same identity schema, so migrating between the two is seamless. It's a practical middle ground between building auth from scratch and locking into a proprietary vendor like Clerk.</content>
English and Turkish are implemented, with locale selection from the request or tenant default
Enterprise SSO is advertised in pricing, but the repository still lists SAML as a roadmap item
Authentication-event delivery is available through webhooks; a complete audit-log export is still planned
Similar to Sooauth:
 Descope